Executive Snapshot
Plain-English definition Responsible AI is the disciplined design, deployment, and oversight of artificial intelligence so that it supports legitimate business purposes, produces reliable and fair outcomes, protects data, remains explainable and controllable, and keeps accountable professionals in charge of consequential insurance decisions.
| Dimension | What Responsible AI Requires |
|---|---|
| Purpose | A documented, legitimate insurance use case with defined users, boundaries, and prohibited uses. |
| Data | Lawful, relevant, representative, secure, and quality-controlled data. |
| Model | Validated performance, documented limitations, monitored drift, and appropriate explainability. |
| People | Named owners, trained users, human review, escalation paths, and decision accountability. |
| Process | Controls across design, procurement, testing, release, monitoring, incident response, and retirement. |
| Outcome | Measurable business value without unacceptable harm, unfairness, privacy loss, or hidden automation. |
Executive Summary
Responsible AI is not a single model feature, policy statement, or compliance checklist. It is an operating discipline that connects business strategy, data governance, model risk management, cybersecurity, legal and regulatory obligations, workflow design, and professional judgment. In Property & Casualty insurance, this discipline is especially important because AI can influence claim triage, severity assessment, litigation monitoring, fraud referrals, underwriting prioritization, policy servicing, customer communications, and management decisions.
The practical goal is not to eliminate all risk. It is to make AI risk visible, measurable, controlled, and proportionate to the business decision. A low-impact document-routing model should not require the same controls as a system that recommends claim settlement ranges or underwriting actions. Responsible AI therefore depends on risk-tiering, clear accountability, auditable evidence, and controls that fit the use case.
For insurers, the strongest model is human-centered: AI continuously analyzes information, explains signals and sources, and recommends actions; licensed, trained, or otherwise accountable professionals retain authority for consequential decisions. This approach improves adoption, supports defensibility, and aligns AI with the way insurers already manage financial, operational, conduct, and model risk.
Quick Facts
- Responsible AI applies to predictive models, generative AI, document intelligence, computer vision, AI agents, and vendor-provided systems.
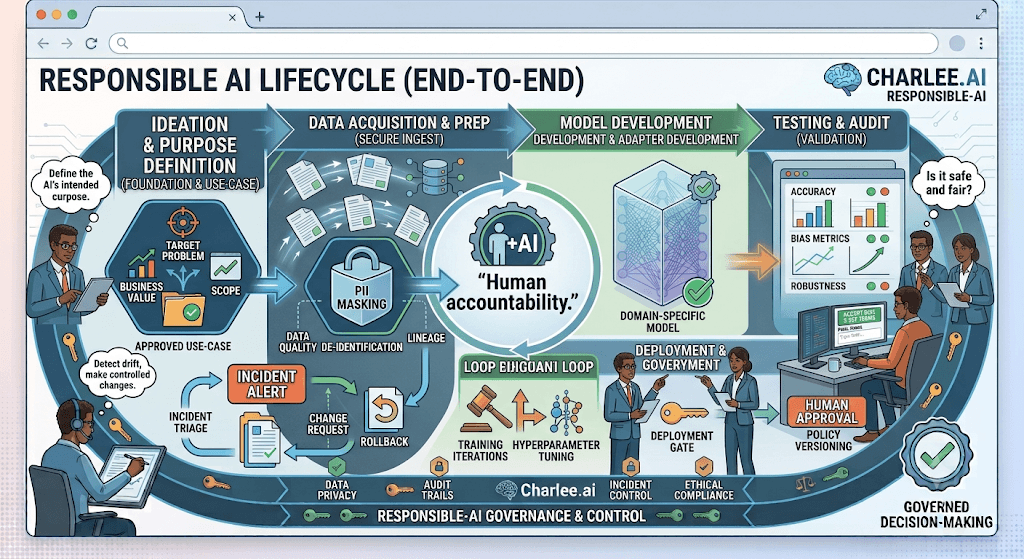
- Governance must cover the full lifecycle—from idea approval and data preparation through deployment, monitoring, change control, and retirement.
- Fairness is use-case specific; it requires testing outcomes, data pathways, and operational impacts rather than relying only on a single statistical metric.
- Explainability should be matched to the audience: developers need technical diagnostics, professionals need decision-relevant reasons, and customers may need clear plain-language explanations.
- Human review must be meaningful. A nominal approval button is not adequate if users lack time, authority, context, or training to challenge the AI.
- Every production AI capability should have a named business owner, technical owner, risk classification, approved purpose, monitoring plan, and incident-response path.
Definitions
Executive Definition
Responsible AI is the enterprise framework for ensuring that artificial intelligence is used for approved purposes, governed according to risk, validated for reliability and fairness, transparent enough for its users, secure and privacy-preserving, and subject to accountable human oversight.
Technical Definition
Responsible AI is a lifecycle control system that combines data governance, model development standards, evaluation, explainability, robustness testing, security controls, access management, audit logging, monitoring, incident management, and controlled change. It applies to both internally developed and third-party AI components, including foundation models and external services.
Insurance Definition
In P&C insurance, Responsible AI means using AI to improve information, prioritization, consistency, and speed while ensuring that coverage, reserving, settlement, underwriting, referral, fraud, and customer decisions remain legally compliant, evidence-based, reviewable, and accountable to qualified insurance professionals.
Responsible AI vs. AI Ethics vs. AI Governance
| Concept | Primary Question | Insurance Example |
|---|---|---|
| AI ethics | What principles should guide behavior? | Avoid unfair treatment, hidden manipulation, or unsupported claim conclusions. |
| AI governance | Who approves, controls, documents, and monitors AI? | Model inventory, ownership, risk tier, review gates, and audit evidence. |
| Responsible AI | How are principles and governance translated into daily operation? | Validated models, documented workflows, human review, monitoring, and incident response. |
Why the Distinction Matters
Ethical principles without operating controls can remain aspirational. Governance without usable workflow design can become administrative overhead. Responsible AI joins the two: it converts values and obligations into practical requirements that teams can execute, test, monitor, and improve.
Why Responsible AI Matters in P&C Insurance
Insurance decisions affect financial protection, recovery from loss, access to coverage, claim experience, and trust. AI can improve these decisions, but it can also amplify weaknesses in historical data, obscure reasoning, create inconsistent treatment, or automate errors at scale. The risk increases when AI-generated output appears authoritative, when users cannot see the underlying evidence, or when responsibilities are unclear.
| Insurance Concern | How AI Can Help | Responsible-AI Requirement |
|---|---|---|
| Claim complexity | Surface changing medical, legal, and exposure signals. | Show evidence, confidence, limitations, and review expectations. |
| Underwriting volume | Prioritize submissions and summarize risk factors. | Prevent proxy discrimination and preserve underwriter authority. |
| Document overload | Extract and summarize large claim and policy files. | Preserve provenance and enable source-level verification. |
| Fraud detection | Identify unusual patterns and connected activity. | Use referrals, not unsupported adverse conclusions; monitor false positives. |
| Customer communication | Draft faster, more consistent responses. | Require approved content, privacy controls, and human review where appropriate. |
| Portfolio management | Detect emerging severity and litigation trends. | Validate aggregation logic and avoid masking local variation. |
Core principle The more consequential the decision, the stronger the evidence, explanation, human oversight, testing, and approval controls should be.
The Responsible AI Operating Model
A mature operating model connects leadership expectations with front-line execution. It defines decision rights, standard artifacts, approval gates, risk tiers, and monitoring responsibilities without requiring every AI initiative to navigate the same level of process.
| Layer | Primary Responsibility | Typical Artifacts |
|---|---|---|
| Board / Executive oversight | Set risk appetite, accountability, and strategic priorities. | Policy, risk appetite, oversight reports, material-risk escalation. |
| Business ownership | Define purpose, workflow, users, outcomes, and acceptable limitations. | Use-case charter, process map, KPI baseline, user controls. |
| AI / Data teams | Design, develop, test, document, and maintain the system. | Model card, data sheet, test results, release package. |
| Risk / Compliance / Legal | Challenge assumptions, assess obligations, and approve controls. | Risk assessment, legal review, fairness review, control requirements. |
| Security / Privacy | Protect data, identities, integrations, and model access. | Threat model, privacy assessment, access design, logging standards. |
| Operations / Users | Apply judgment, review output, document decisions, and report issues. | SOPs, training, feedback, overrides, incident reports. |
| Audit / Independent validation | Assess design and operating effectiveness. | Validation report, audit findings, remediation tracking. |
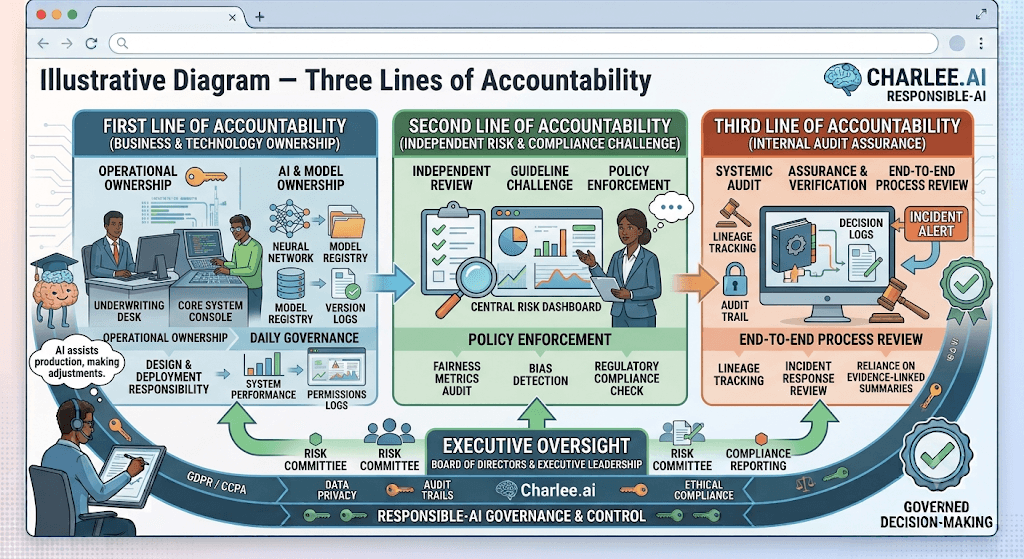
Three Lines of Accountability
- First line: Business and technology teams own the use case, controls, performance, and daily operation.
- Second line: Risk, compliance, privacy, security, and legal functions establish standards and provide independent challenge.
- Third line: Internal audit or equivalent independent review evaluates whether governance and controls are designed and operating effectively.
Core Principles of Responsible AI
Purpose and legitimacy
Use AI only for a documented, approved business purpose. Prevent uncontrolled secondary uses and function creep.
Accountability
Assign named owners who can approve, challenge, pause, change, and retire the system.
Human agency and oversight
Keep people in meaningful control of consequential insurance decisions.
Fairness and non-discrimination
Evaluate whether data, features, models, and workflows create unjustified differences in treatment or outcomes.
Transparency and explainability
Make the system, its role, evidence, limits, and decision logic understandable to the appropriate audience.
Reliability and safety
Validate accuracy, robustness, calibration, failure modes, and operational resilience before and after deployment.
Privacy and data stewardship
Limit data to what is appropriate, protect confidentiality, manage retention, and control access.
Security and misuse prevention
Defend against unauthorized access, prompt injection, data leakage, model abuse, and unsafe tool execution.
Contestability and recourse
Provide practical ways to question, correct, override, or escalate AI-supported outcomes.
Continuous monitoring and improvement
Track performance, fairness, drift, incidents, and business impact throughout the lifecycle.
Risk Classification and Proportionate Controls
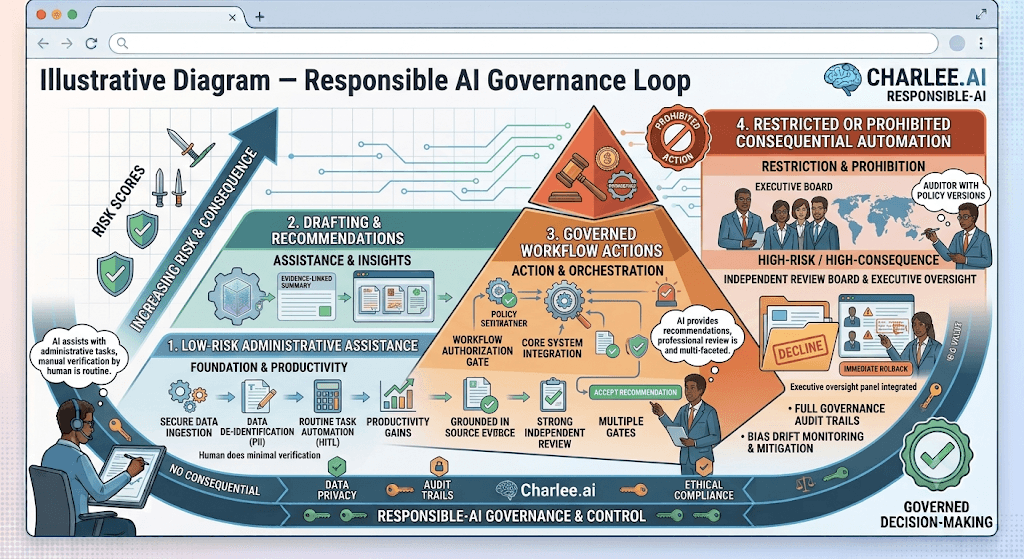
A risk-tiering framework allows insurers to focus the strongest controls on the systems that can create the greatest harm. Classification should consider decision impact, autonomy, affected population, data sensitivity, regulatory exposure, financial materiality, model complexity, and reversibility.
| Risk Tier | Typical Use | Illustrative Controls |
|---|---|---|
| Tier 1 — Low | Internal search, duplicate detection, non-consequential routing. | Basic owner, data approval, testing, logging, user guidance. |
| Tier 2 — Moderate | Claim prioritization, document summaries, underwriting triage. | Formal validation, source evidence, human review, monitoring, change approval. |
| Tier 3 — High | Reserve recommendations, settlement support, fraud referrals, underwriting recommendations. | Independent validation, fairness testing, enhanced explanations, strict access, override tracking, frequent monitoring. |
| Tier 4 — Restricted / Prohibited | Unreviewed adverse claim or underwriting decisions; uses outside legal or policy boundaries. | Do not deploy, or redesign to preserve lawful, accountable human decision-making. |
Risk Assessment Questions
- What decision or workflow can the AI influence?
- Who may be affected, and what is the severity of a wrong result?
- Can a person detect, challenge, and reverse the outcome?
- Does the system use sensitive, protected, or highly confidential data?
- Could a feature act as a proxy for an inappropriate factor?
- How autonomous is the system, and what external tools can it invoke?
- What evidence will be retained to reconstruct the result?
- What happens when the model, data, integration, or vendor service fails?
Responsible AI Across the Lifecycle
| Lifecycle Stage | Required Questions | Evidence |
|---|---|---|
| Ideation | Is the purpose legitimate, valuable, and suitable for AI? | Use-case charter, alternatives analysis, preliminary risk tier. |
| Data preparation | Is data lawful, relevant, representative, and controlled? | Data inventory, lineage, quality report, privacy review. |
| Design and development | Are objectives, constraints, users, and failure modes explicit? | Architecture, feature review, prompt design, threat model. |
| Validation | Does the system meet technical, business, fairness, and operational requirements? | Test plan, benchmark results, scenario testing, independent challenge. |
| Deployment | Are access, logging, training, fallback, and approvals complete? | Release checklist, SOPs, training records, rollback plan. |
| Monitoring | Is performance stable, useful, fair, and secure in production? | Dashboards, drift alerts, override analysis, incident logs. |
| Change management | Are changes tested and approved according to impact? | Version record, change assessment, regression testing. |
| Retirement | Are dependencies, data, records, and user communications handled? | Decommission plan, archival evidence, access removal. |
Data Responsibility
Responsible AI begins with data responsibility. Insurers should understand where data came from, why it is appropriate, how it was transformed, what populations it represents, and what limitations may affect outcomes. Historical data can encode prior business practices, missing documentation, inconsistent reserve behavior, geographic concentration, or differences in access to treatment and representation.
Data Control Checklist
- Document source systems, ownership, lineage, refresh timing, and permitted uses.
- Measure completeness, consistency, timeliness, accuracy, and label quality.
- Review sensitive attributes and potential proxy variables.
- Test representation across relevant lines, jurisdictions, claim types, severity bands, and customer segments.
- Control training, evaluation, production, and vendor-access datasets separately.
- Apply retention, minimization, encryption, access, masking, and deletion requirements.
- Preserve provenance so users can trace outputs back to source records where appropriate.
Data Control Checklist
Insurance reality Data that is operationally useful is not automatically appropriate for every AI purpose. A feature may be predictive yet still require legal, fairness, privacy, or conduct review.
Fairness and Non-Discrimination
Fairness is not a single mathematical score. It is a structured inquiry into whether an AI-enabled process creates unjustified differences in access, treatment, error rates, burden, or outcomes. In insurance, the assessment should consider both model performance and the surrounding workflow—including how referrals are investigated, how exceptions are handled, and whether certain groups face more frequent review or delay.
| Fairness Lens | Question | Illustrative Measure |
|---|---|---|
| Data representation | Are relevant populations adequately represented? | Coverage by segment, missingness, label consistency. |
| Performance parity | Are error rates materially different across groups? | False-positive and false-negative rates, calibration. |
| Outcome review | Do recommendations create unjustified disparities? | Referral rate, approval rate, cycle time, override rate. |
| Process fairness | Can users understand and challenge the result? | Explanation quality, escalation access, time to correction. |
| Feature appropriateness | Are inputs legitimate and necessary for the purpose? | Feature review, proxy analysis, sensitivity tests. |
Practical Fairness Process
Define the decision and the potential harm.
Identify relevant populations and comparison groups with legal and compliance guidance.
Assess data quality, representation, labels, and feature pathways.
Compare performance and operational outcomes across groups.
Investigate root causes rather than relying only on aggregate metrics.
Mitigate through data, model, threshold, workflow, or policy changes.
Document conclusions, residual risk, approvals, and monitoring requirements.
Transparency, Explainability, and Evidence
Transparency explains what the system is, where it is used, what it can and cannot do, and who is accountable. Explainability provides reasons for a specific output or overall model behavior. Evidence allows a user or reviewer to verify the facts, documents, and signals supporting the output. Responsible insurance AI often needs all three.
| Audience | What They Need |
|---|---|
| Claims professional | Relevant signals, source documents, confidence, change history, and recommended next action. |
| Underwriter | Risk factors, source data, appetite context, uncertainties, and referral rationale. |
| Manager | Portfolio patterns, performance, exceptions, overrides, and operational impact. |
| Model validator | Data lineage, methodology, benchmarks, limitations, sensitivity, and failure modes. |
| Customer / claimant | Clear, accurate, non-technical communication appropriate to the decision and applicable requirements. |
| Auditor / regulator | Reconstructable records showing purpose, controls, testing, approvals, monitoring, and decision accountability. |
Evidence-Centered Design
- Link generated summaries to the underlying documents and passages.
- Show timestamps and changes when decisions depend on evolving claim information.
- Distinguish observed facts, model inferences, and professional conclusions.
- Expose uncertainty and missing information rather than presenting false precision.
- Retain model version, data version, prompt or configuration, retrieved sources, and user action when needed for auditability.
Human-in-the-Loop Governance
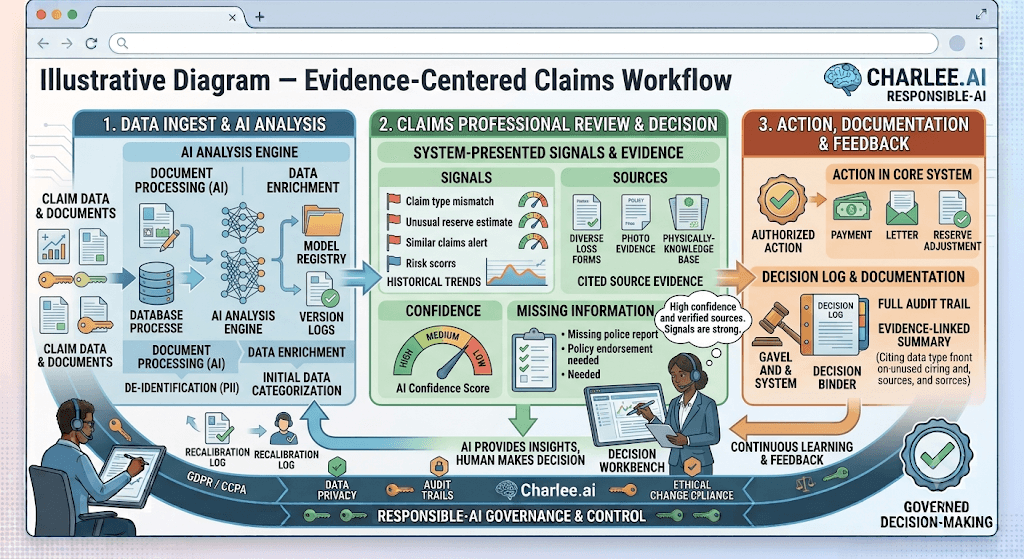
Human oversight is meaningful only when users have the information, authority, competence, and time to exercise judgment. The strongest workflow does not ask people to rubber-stamp AI. It presents prioritized evidence, explains why attention is needed, allows users to inspect sources, captures professional decisions, and learns from structured feedback.
| Weak Oversight | Strong Oversight |
|---|---|
| User sees only a score. | User sees drivers, evidence, confidence, and limitations. |
| Approval is required but rarely challenged. | Overrides are expected when evidence or context supports them. |
| No clear owner for errors. | Business and technical owners are named and accountable. |
| AI output is copied into records without verification. | Professional confirms facts and distinguishes AI output from final judgment. |
| Feedback disappears into free text. | Overrides, corrections, and incidents are captured in structured form. |
Human Oversight Design Questions
- Which decisions must remain exclusively human?
- What information must be shown before a user can act?
- When is secondary review required?
- How are disagreements, overrides, and escalations recorded?
- What training is required for each user role?
- How does the system fail safely when confidence is low or data is incomplete?
Reliability, Validation, and Monitoring
Responsible AI requires evidence that a system works for its intended purpose—not merely that it performs well on a development dataset. Validation should test technical accuracy, business usefulness, operational reliability, fairness, robustness, explainability, integration behavior, and human interaction.
| Validation Area | Examples |
|---|---|
| Technical performance | Discrimination, calibration, precision, recall, extraction accuracy, hallucination rate. |
| Business performance | Cycle time, prioritization value, missed-risk reduction, productivity, outcome quality. |
| Operational performance | Latency, uptime, integration failures, fallback behavior, queue impact. |
| Robustness | Missing data, unusual documents, adversarial inputs, distribution shift, catastrophe conditions. |
| Human factors | Comprehension, appropriate reliance, override quality, workload, user error. |
| Fairness | Segment-level performance, outcome disparity, referral burden, correction access. |
| Security and privacy | Access controls, data leakage, prompt injection, tool misuse, retention compliance. |
Monitoring Signals
- Input and feature drift
- Output distribution changes
- Performance and calibration decay
- Segment-level error differences
- Override and disagreement trends
- Complaint or escalation patterns
- Data-quality degradation
- Latency and integration failures
- Security alerts and anomalous access
- Vendor model or configuration changes
Security, Privacy, and Misuse Prevention
AI expands the attack surface because models may receive untrusted documents, retrieve enterprise content, call tools, generate executable instructions, or interact with external services. Responsible AI therefore requires security-by-design and least-privilege access at the data, model, application, integration, and user layers.
| Risk | Control Examples |
|---|---|
| Data leakage | Private deployment, data minimization, encryption, DLP, contractual restrictions, redaction. |
| Prompt injection | Content isolation, tool allowlists, instruction hierarchy, retrieval filtering, adversarial testing. |
| Unauthorized actions | Least privilege, approval gates, transaction limits, strong identity, immutable logs. |
| Model misuse | Role-based access, approved-use policy, monitoring, output restrictions, abuse detection. |
| Vendor dependency | Due diligence, audit rights, data terms, model-change notice, continuity and exit plans. |
| Sensitive output | Post-processing, content filters, source checks, restricted fields, human review. |
Responsible AI for Predictive Models
Predictive models estimate future outcomes or classify risk. Responsible use requires careful attention to label quality, temporal leakage, calibration, threshold selection, proxy variables, segment performance, and the difference between correlation and an actionable insurance conclusion.
- Use time-aware development and validation to prevent future information from leaking into training.
- Calibrate risk scores so that predicted probabilities correspond to observed outcomes.
- Test thresholds in the actual workflow, not only in offline analytics.
- Explain the strongest drivers and confirm they are appropriate for the use case.
- Monitor false negatives as well as false positives, especially where missed claims create severe exposure.
- Retain human authority for reserves, settlement, coverage, underwriting terms, and fraud conclusions.
Responsible AI for Generative AI and RAG
Generative AI creates new text, summaries, answers, or recommendations. Responsible use depends on grounding, source verification, privacy controls, prompt security, output constraints, and careful separation between generated assistance and final insurance judgment.
| Risk | Responsible Design |
|---|---|
| Hallucination | Ground answers in approved sources; require citations; abstain when evidence is insufficient. |
| Outdated knowledge | Use governed retrieval, effective-date metadata, and source freshness controls. |
| Confidentiality | Restrict model access, prevent training on customer data without authorization, and log data flows. |
| Prompt inconsistency | Use versioned templates, test suites, approved examples, and controlled changes. |
| Overreliance | Train users, show uncertainty, require source review, and analyze automation bias. |
| Unsafe retrieval | Apply authorization-aware search, metadata filters, and document-level access controls. |
Responsible AI for AI Agents
AI agents can plan, retrieve information, call tools, and take actions. Their autonomy creates additional risks: incorrect sequencing, unauthorized transactions, tool misuse, propagation of errors, and difficulty reconstructing multi-step behavior. Controls should focus on permissions, bounded goals, approved tools, transaction limits, intermediate checkpoints, and complete action logs.
Agent safety rule No agent should have broader authority than the human role it supports, and consequential actions should require explicit approval unless a narrow, pre-approved exception is justified and monitored.
Claims Case Study: Severity and Litigation Monitoring
A workers’ compensation carrier deploys AI to identify claims with emerging severity, attorney involvement, treatment escalation, reserve pressure, or litigation risk. The system reviews structured claim data and incoming documents, then prioritizes files for professional attention.
Responsible Design
| Control Area | Implementation |
|---|---|
| Purpose | Prioritize review and surface evidence; do not autonomously set reserves or settlement strategy. |
| Data | Use approved claim, medical, legal, and document data with lineage and quality checks. |
| Model | Validate performance by jurisdiction, injury type, claim age, and severity band. |
| Explanation | Show changing signals, source documents, timeline, confidence, and missing information. |
| Human oversight | Examiner or manager decides action; significant reserve or settlement changes follow existing authority rules. |
| Fairness | Test referral and error patterns across relevant groups and investigate operational disparities. |
| Monitoring | Track missed severe claims, false alerts, user overrides, cycle time, reserve adequacy, and complaints. |
| Incident response | Pause recommendations when data feeds fail or model behavior departs from approved limits. |
Expected Business Value
- Earlier recognition of deteriorating claims
- More consistent portfolio monitoring
- Better allocation of specialist attention
- Faster review of new medical and legal evidence
- Improved documentation of why actions were taken
Underwriting Case Study: Commercial Submission Triage
A commercial insurer uses AI to extract submission data, summarize operations, compare information with appetite guidelines, and prioritize submissions for underwriter review. The system does not make final eligibility, pricing, or terms decisions.
| Control Area | Implementation |
|---|---|
| Purpose | Reduce administrative effort and improve prioritization. |
| Data | Validate extraction and source links; separate broker statements from verified external data. |
| Model | Test across classes, account sizes, document types, and broker formats. |
| Fairness | Review features and outcomes for inappropriate proxies or unjustified geographic effects. |
| Explanation | Show appetite matches, conflicts, missing data, and source evidence. |
| Human oversight | Underwriter retains authority for risk selection, pricing, terms, and referral. |
| Monitoring | Track extraction errors, referral patterns, hit rate, turnaround time, and underwriter overrides. |
| Change control | Re-test when appetite rules, product strategy, forms, or external data sources change. |
Business Benefits
| Benefit | How Responsible AI Creates Value |
|---|---|
| Trust and adoption | Users are more likely to rely appropriately on systems they understand and can challenge. |
| Better decisions | Evidence, explanations, and human review improve the quality of action. |
| Operational resilience | Monitoring, fallback, and incident controls reduce disruption and hidden failure. |
| Regulatory defensibility | Documented purpose, testing, approvals, and records support examination and audit. |
| Scalable innovation | Reusable standards and risk tiers allow more AI initiatives to move safely into production. |
| Vendor control | Due diligence and contractual requirements reduce dependency and data risk. |
| Enterprise learning | Structured feedback, overrides, and incidents improve future models and workflows. |
Common Failure Modes
| Failure Mode | Why It Fails | Better Approach |
|---|---|---|
| Policy-only governance | Principles do not change daily behavior. | Embed controls in approvals, workflows, systems, and monitoring. |
| One-size-fits-all review | Low-risk projects are slowed while high-risk details may be missed. | Use risk tiers and proportionate evidence. |
| Accuracy-only testing | A model can be accurate but unfair, brittle, insecure, or unusable. | Validate technical, business, fairness, human, and operational performance. |
| Nominal human review | Users cannot meaningfully challenge the output. | Provide evidence, training, authority, time, and escalation. |
| Uncontrolled vendor AI | The insurer lacks visibility into data use and model changes. | Perform due diligence and require contractual and monitoring controls. |
| No post-deployment ownership | Performance deteriorates without action. | Assign owners, thresholds, cadence, escalation, and retirement criteria. |
Implementation Blueprint
Establish executive sponsorship, policy, risk appetite, and decision rights.
Create an enterprise AI inventory that includes internal, embedded, and third-party systems.
Define risk tiers and the minimum evidence required for each tier.
Standardize use-case charters, data assessments, model cards, validation reports, and release checklists.
Integrate privacy, security, compliance, legal, and model-risk review into the delivery lifecycle.
Design human oversight and user experience before finalizing the model.
Build benchmark datasets and scenario tests that reflect real insurance conditions.
Require production monitoring, override capture, incident response, and controlled change.
Train executives, developers, validators, managers, and front-line users according to role.
Review the framework regularly as technology, regulation, products, and business practices evolve.
Executive Decision Guide
| Question | Proceed When | Pause or Redesign When |
|---|---|---|
| Is the purpose clear? | The use case, users, benefits, and prohibited uses are documented. | The system may be reused for undefined or adverse purposes. |
| Is AI appropriate? | AI adds measurable value beyond simpler rules or workflow changes. | The problem can be solved more safely and transparently without AI. |
| Is data suitable? | Data is lawful, relevant, representative, and controlled. | Lineage, quality, permission, or bias concerns are unresolved. |
| Can users exercise judgment? | They receive evidence, training, authority, and escalation paths. | The workflow encourages automatic acceptance. |
| Can the system be validated? | Success criteria, benchmarks, segments, and failure tests are defined. | The team cannot measure material risks or reconstruct outcomes. |
| Can it be monitored and stopped? | Owners, thresholds, alerts, rollback, and incident plans exist. | There is no reliable way to detect or contain harmful behavior. |
Charlee.ai Perspective
For P&C insurance, Responsible AI should be designed around the professional workflow—not added after a model is built. The most valuable systems continuously analyze claim and underwriting information, surface material changes, explain why they matter, and connect users to the supporting evidence. Professionals retain authority, document decisions, and provide feedback that improves the system over time.
This people-plus-AI model is especially important in claims. Claims are dynamic, evidence-rich, and operationally complex. A responsible platform should help professionals see emerging severity, litigation, treatment, documentation, and reserve signals earlier while avoiding unsupported conclusions and preserving the examiner’s accountability for coverage, reserves, strategy, and settlement.
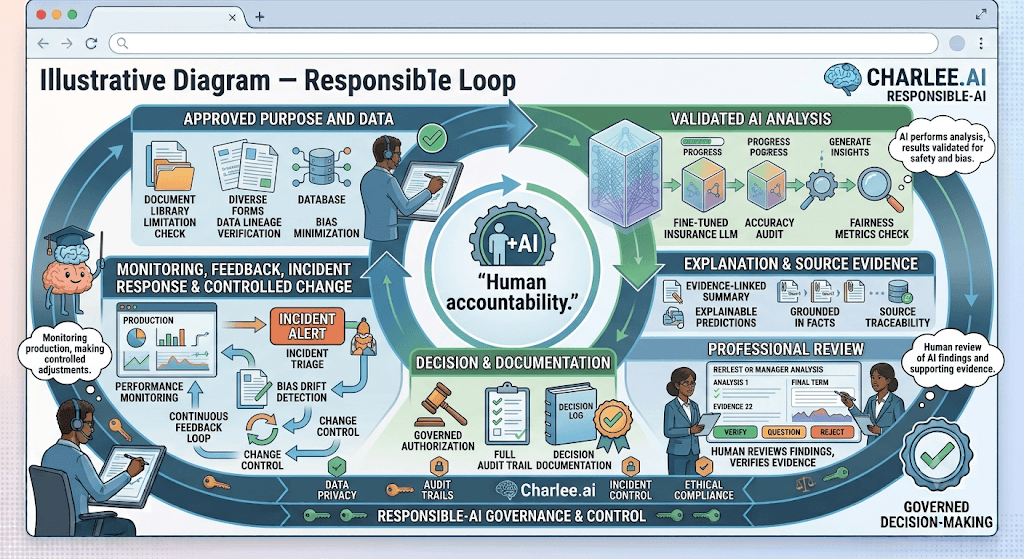
Charlee.ai responsible-AI pattern Approved purpose and data → validated AI analysis → explanation and source evidence → professional review → decision and documentation → monitoring, feedback, incident response, and controlled change.
Key Takeaways
- Responsible AI is an operating discipline, not a policy statement.
- Controls should be proportionate to the use case and consequence of error.
- Insurance AI should augment professional judgment and preserve accountable decision authority.
- Data quality, fairness, explainability, security, privacy, and reliability must be addressed together.
- Human review must be meaningful, evidence-centered, trained, and empowered.
- Production monitoring, incident response, and controlled change are essential.
- A reusable governance framework enables faster—not slower—responsible innovation.
Plain-English definition Responsible AI is the disciplined design, deployment, and oversight of artificial intelligence so that it supports legitimate business purposes, produces reliable and fair outcomes, protects data, remains explainable and controllable, and keeps accountable professionals in charge of consequential insurance decisions.
Frequently Asked Questions
Responsible AI is the disciplined design, deployment, and oversight of AI so that it is lawful, reliable, fair, transparent, secure, privacy-preserving, and accountable to people.
No. Compliance is essential, but Responsible AI also covers business purpose, technical reliability, fairness, security, human factors, operational resilience, and ethical use.
Ownership is shared, but accountability must be explicit. Business owners own the use case; technical teams own implementation; risk functions provide challenge; executives set policy and risk appetite.
No. Controls should be proportionate to the decision impact, autonomy, data sensitivity, affected population, and reversibility of error.
Some low-risk administrative actions may be automated, but consequential coverage, claim, settlement, reserve, fraud, underwriting, and pricing decisions require careful legal analysis, governance, and meaningful human accountability.
It means the reviewer has enough information, time, authority, training, and context to question, override, and escalate the AI output.
By examining data, features, model performance, workflow, and outcomes across relevant groups, then investigating and mitigating unjustified differences.
Typical artifacts include a use-case charter, data sheet, model card, risk assessment, validation report, release checklist, monitoring plan, incident log, and change record.
Use approved data, grounding, citations, privacy controls, prompt security, output constraints, human review, and monitoring for hallucination and misuse.
The explanation must fit the audience and decision. Professionals need reasons and evidence; validators need technical detail; customers may need clear plain-language communication.
Apply due diligence, contractual controls, data restrictions, security review, performance testing, model-change notice, audit rights, continuity planning, and ongoing monitoring.
It is a controlled record of AI systems, owners, purposes, risk tiers, models, data, vendors, deployment locations, approvals, and lifecycle status.
Performance, calibration, drift, fairness, data quality, overrides, user behavior, complaints, security events, incidents, and business value.
When performance breaches limits, data feeds fail, material unfairness appears, security is compromised, the approved purpose changes, or the system cannot be safely monitored.
It improves adoption, reduces rework and incidents, supports scaling, strengthens defensibility, and directs investment toward systems that create reliable business value.
No. It may still use inappropriate data, create unfair outcomes, be insecure, lack explanations, or encourage harmful automation.
At least according to the system’s risk tier and whenever material changes occur in data, models, workflows, regulation, vendors, or business purpose.
Create an AI inventory, define risk tiers and ownership, select a small number of representative use cases, and establish reusable lifecycle controls before scaling.